Latest Publications
TECHNICAL ARTICLES
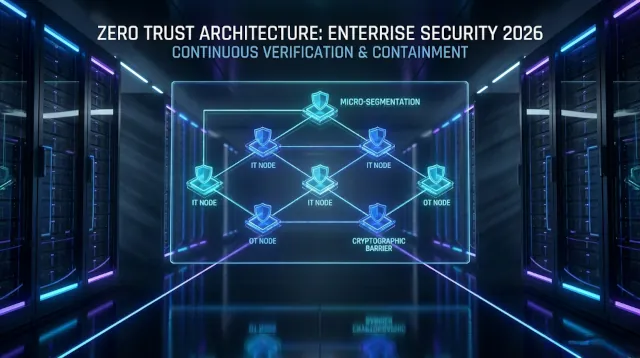
Zero Trust in 2026 — Beyond the Hype
A practical, implementation-focused look at zero trust architecture for enterprise and OT environments.
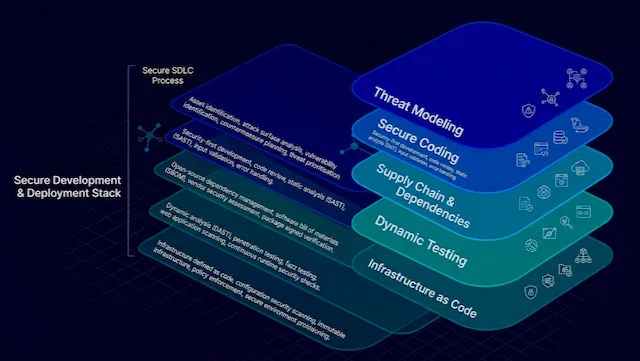
Secure SDLC — Integrating Security into DevOps Pipelines
How to embed security into your software development lifecycle without slowing delivery. Practical controls for modern DevOps environments.
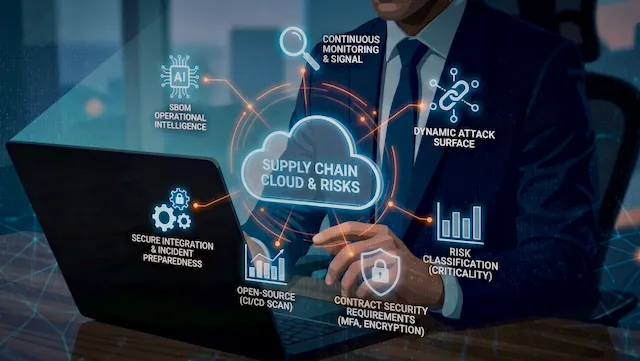
Supply Chain Risk Management in Modern Software Ecosystems
How to manage third-party and software supply chain risk without slowing development. Practical controls for modern ecosystems.
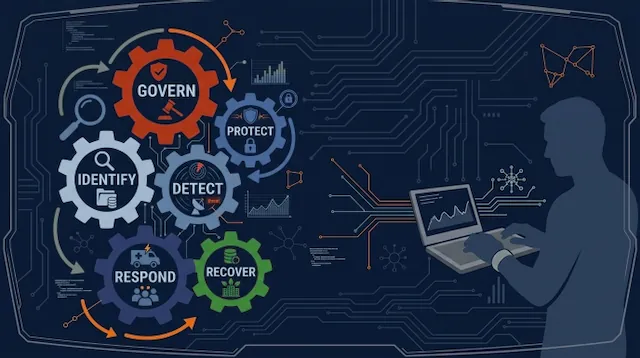
NIST CSF Adoption — A Practical Guide
How to adopt the NIST Cybersecurity Framework in a way that improves security posture, aligns teams, and supports compliance.
ISO 27001 Readiness Checklist for Enterprises
A structured, no-fluff checklist to prepare your organization for ISO 27001 certification. For security leaders and compliance teams.
Incident Response Playbook for Critical Infrastructure
A structured approach to incident response for environments where downtime, safety, and reputation are non-negotiable.
OT Security — Bridging IT and Operational Systems
How to secure the convergence of IT and OT without disrupting operations. Practical guidance for industrial environments.
Cloud Security Posture Assessment for Multi-Cloud Environments
How to assess and improve security posture across multiple cloud providers without losing visibility or control.
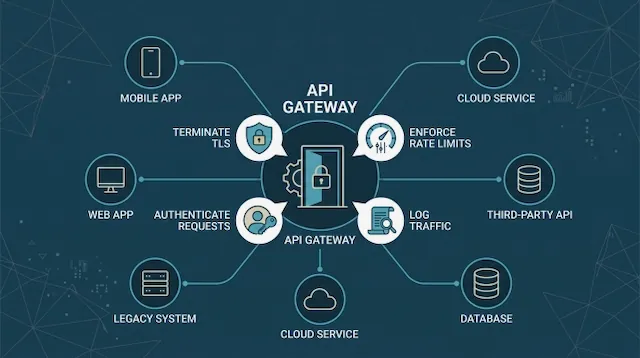
API Security Best Practices for Microservice Architectures
Practical guidance to secure APIs in microservice environments—authentication, authorization, resilience, and defence-in-depth.
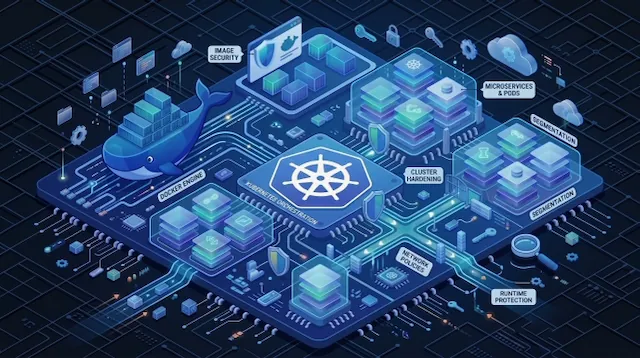
Container and Kubernetes Security Hardening Guide
A concise, practical guide to hardening containers and Kubernetes clusters against common threats and misconfigurations.
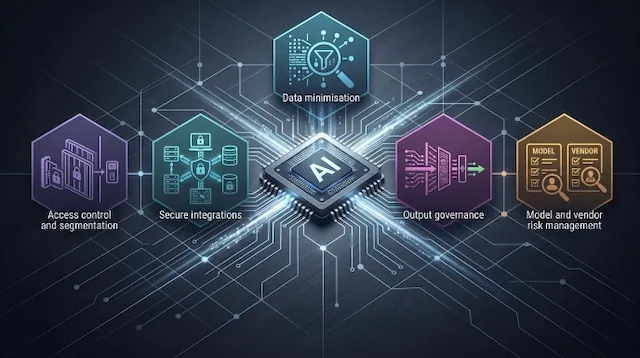
Privacy-Preserving Design for AI and Generative Systems
How to integrate privacy, data protection, and security into AI and generative systems without stifling innovation.
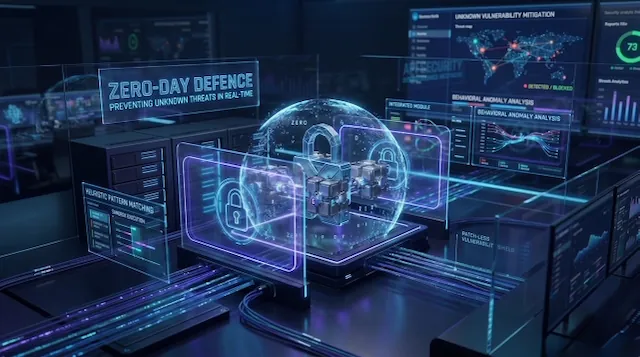
Defending Against Zero-Day Threats Without Perfect Intelligence
Practical strategies to reduce the impact of zero-day vulnerabilities when threat intelligence is incomplete or delayed.
Categories
Explore our technical research organized by core cybersecurity discipline.
Architecture
Zero trust implementations, multi-cloud posture, and privacy-preserving generative system design.
Compliance
ISMS certification readiness, audit preparation, evidence frameworks, and continuous compliance.
IT/OT Security
Operational technology boundaries, industrial control protocols, container hardening, and cluster protection.
Secure Development
DevSecOps pipeline integration, automated static analysis, threat modeling, and microservice API security.
Risk & Governance
NIST Cybersecurity Framework adoption, executive communication, software supply chain risk, and SBOMs.
Incident Response
Critical infrastructure playbooks, containment workflows, root cause forensics, and zero-day threat response.