ADVISE. DESIGN. SECURE.

Sovereign Assurance & Secure Blueprints.

Bringing the strict operational rigor of defense-sector cybersecurity to critical enterprise architectures. Oslys builds and protects digital infrastructure for businesses that cannot afford a breach.

Core Engineering Principles

Defence-Grade Security Engineering

Engineered Clarity. Strategic Security. Zero Wasted Effort.

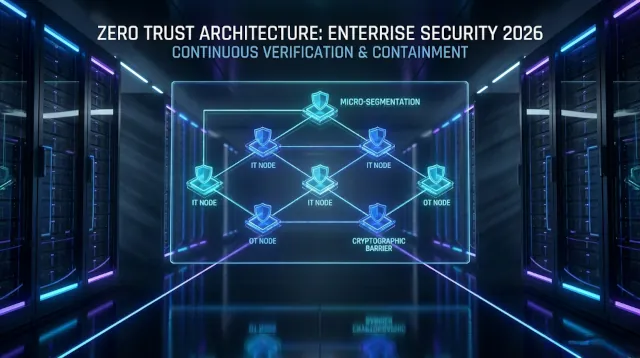
Zero Trust Architecture

Assume breach. Enforce least privilege.

  • •Continuous authentication across all operational layers.
  • •Micro-segmentation designed to eliminate lateral movement threat vectors.
  • •Dynamic, policy-driven access controls tailored to complex workflows.
Compliance by Design

Built to meet standards, not bolted on.

  • •Native alignment with ISO 27001, NIST 800-53, SOC 2, FedRAMP.
  • •Technical controls fully documented, transparent, and auditable.
  • •End-to-end certification support from initial design to final audit.

Operational Velocity

Security that accelerates workflows.

  • •Lightweight control planes that minimise organisational friction.
  • •Automated policy enforcement to eliminate manual bottlenecking.
  • •Engineered to sustain sub-millisecond system latency requirements.
Operational Engagement Model

We embed as an elite external engineering and architecture partner when your systems demand uncompromising trust, scalability, or structural transformation.

1

Root Cause Isolation

Pinpoint and neutralise underlying architectural vulnerabilities behind recurring technical failures.

2

Structural Simplification

Streamline and optimise existing system architecture before introducing costly, redundant tooling.

3

Operational Alignment

Unify distributed systems, data pipelines, and automation directly around business-critical workflows.

Service Pillars

We engineer the blueprints, build the documentation suites, and advise your teams on secure design.

Assessment & Audit Readiness

Deep-dive technical evaluations and institutional-grade evidence preparation to guarantee 100% compliance readiness before third-party external auditors arrive.

Framework Gap Analysis

Technical assessments against Essential Eight, ISM, and ISO 27001 benchmarks.

Physical & OT Security Assessments

Hardening the physical-digital interface across critical infrastructure nodes.

Supply Chain & Audit-Ready Evidence

Auditing upstream software vectors and compiling immutable compliance vaults.

ISO 27001 ISMS Controls

Institutional information security management systems

NIST 800-53 & ISM Baseline

Government & critical infrastructure security baselines

Essential Eight Strategies

Targeted mitigation strategies for cyber intrusions

Governance, Risk & Compliance

Aligning complex enterprise and sovereign operations with strict international standards without sacrificing speed or operational flexibility.

Global Framework Alignment

Native alignment with Essential Eight, ISM, ISO 27001, NIST 800-53 & ISO 42001 AI Security.

Enterprise Process Design

Embedding continuous policy enforcement and zero-friction compliance telemetry.

Strategic Risk Roadmaps

Translating complex legal mandates into structured, actionable engineering tasks.

Secure System Architecture

Architecting, hardening, and scaling resilient infrastructure with zero trust enclaves, threat modelling, and AI guardrails for mission-critical operations.

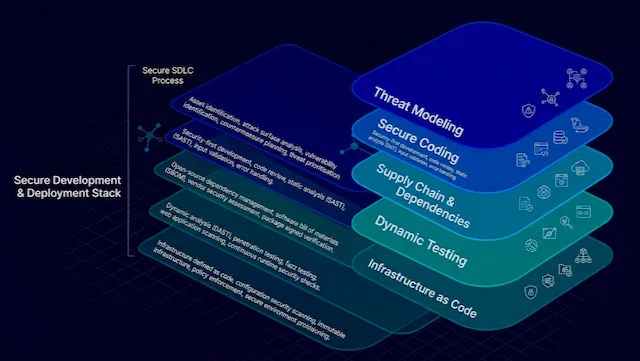
Threat Modelling & Secure SDLC

Eliminating structural vulnerabilities early in product development lifecycle.

Container & Network Micro-Segmentation

Hardening cloud-native environments and zero-trust communication paths.

AI Guardrails & LLM Defence

Deploying robust prompt sanitization and ML pipeline containment safeguards.

AI Guardrails Micro-Segmentation Threat Modelling

seamlessly understand, operate, and scale."

Insights

Insights from our team

Deep-dives into current trends, security insights, frameworks and field notes.

Zero Trust in 2026 — Beyond the Hype

Zero Trust in 2026 — Beyond the Hype

A practical, implementation-focused look at zero trust architecture for enterprise and OT environments.

Architecture
#zero-trust #identity-security
Secure SDLC — Integrating Security into DevOps Pipelines

Secure SDLC — Integrating Security into DevOps Pipelines

How to embed security into your software development lifecycle without slowing delivery. Practical controls for modern DevOps environments.

Secure Development
#sdlc #devsecops
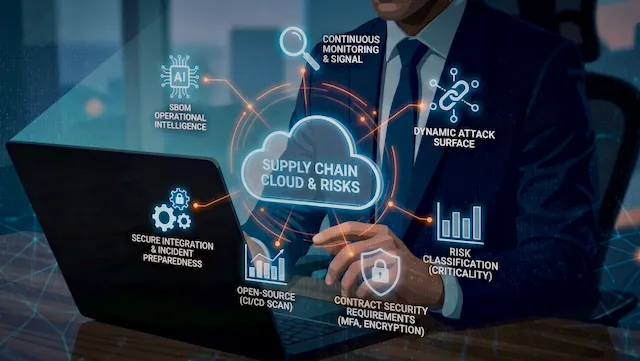
Supply Chain Risk Management in Modern Software Ecosystems

Supply Chain Risk Management in Modern Software Ecosystems

How to manage third-party and software supply chain risk without slowing development. Practical controls for modern ecosystems.

Risk & Governance
#supply-chain-security #sbom

Ready to Secure Your Infrastructure?

Schedule a confidential architectural briefing with our team. Zero sales pressure — just direct engineering insight and actionable risk mitigation strategies.

Book a Technical Briefing

We offer a free 30-minute discovery call.

Book Consultation